





Australian Privacy Principle 3.6 requires you to collect personal information only from the individual, unless collecting it that way is unreasonable… [...]
OpenAI appears to have broken no laws when a rogue artificial intelligence agent gained unauthorised access to Medicare data, with the federal … [...]
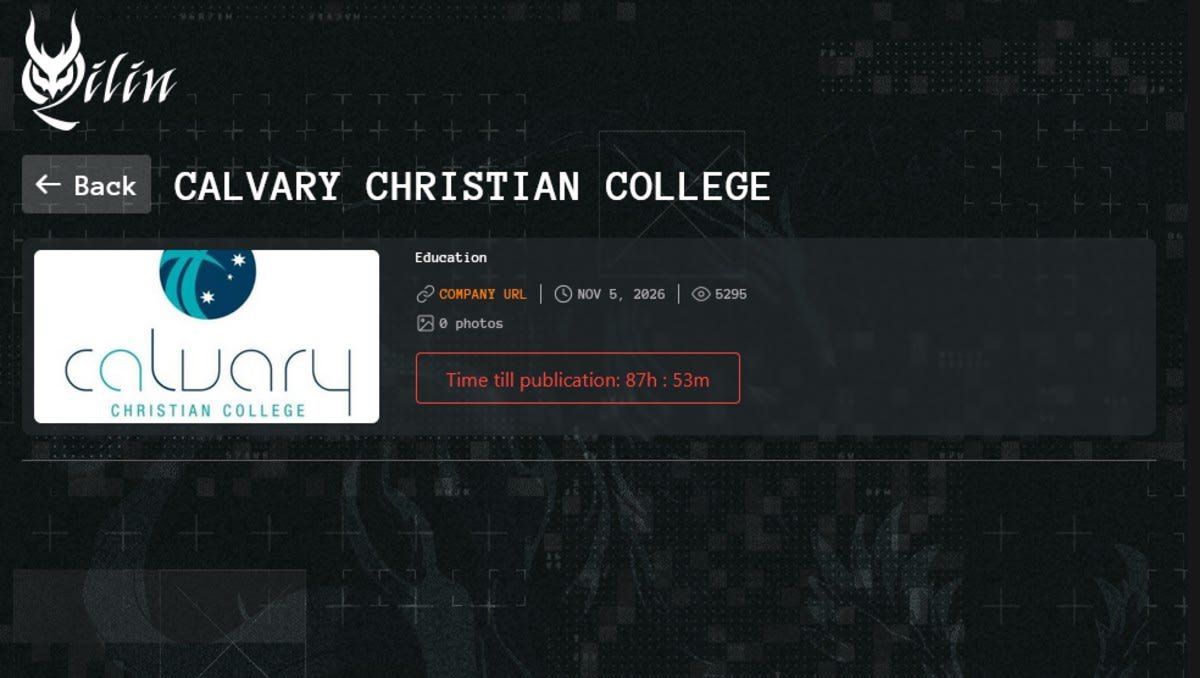
The school says the system holding permission forms was affected by the attack, as the Qilin ransomware group threatens to publish data online. • Tue, … [...]
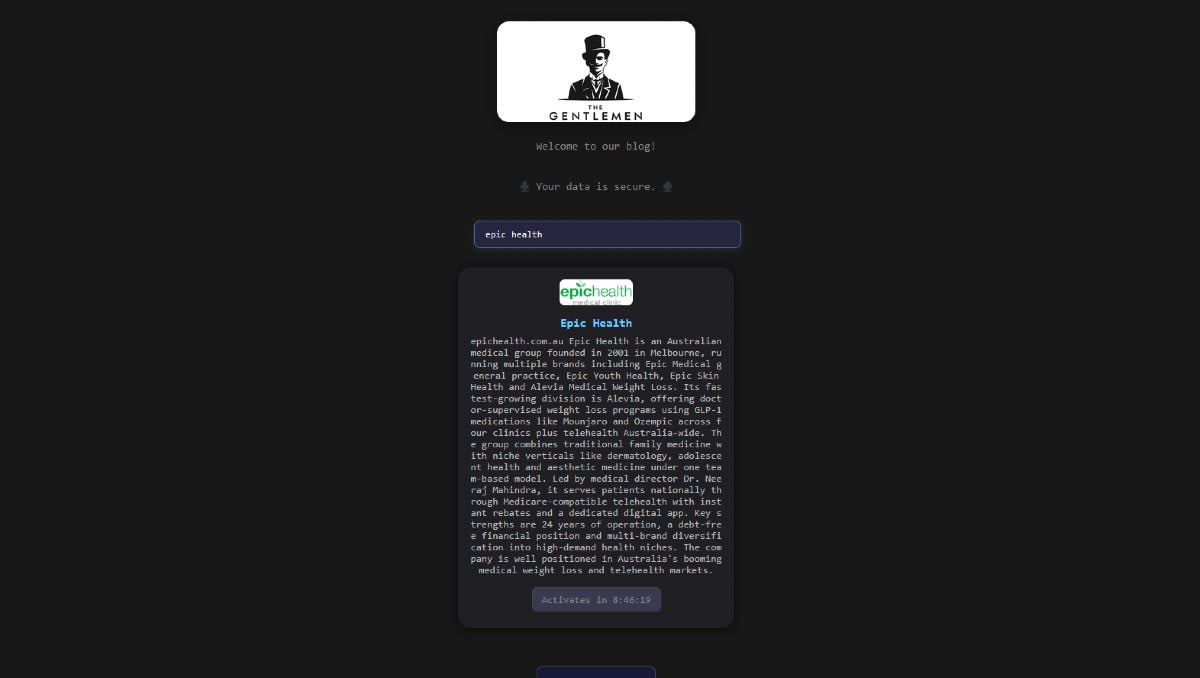
The Victorian healthcare provider says patient data was compromised as an investigation into the scope of the incident continues. • Thu, 05 Nov 2026 • … [...]
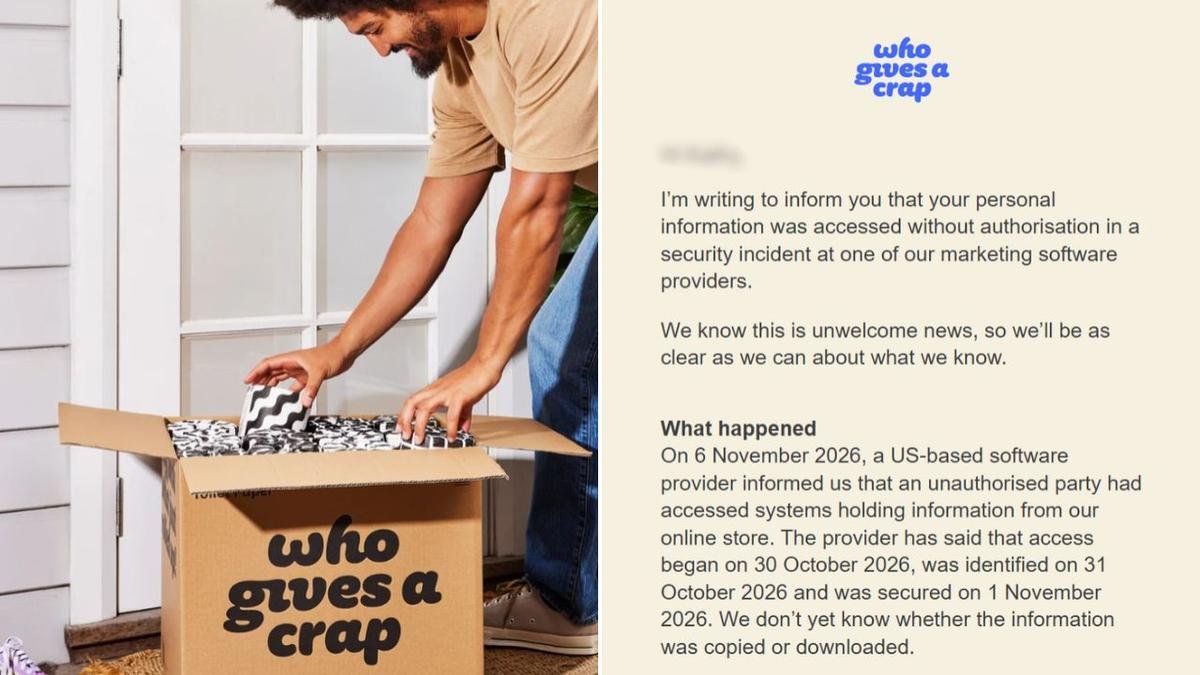
Australian toilet paper company Who Gives A Crap has warned customers their personal information was accessed without authorisation following a cyber … [...]
New statistics from the National Anti-Scam Centre show that buying and selling scams accounted for 58.7% of Scamwatch reports involving a financial … [...]
NT Health has issued a ban on smart glasses at all of its clinical sites, as part of an internal department review into its privacy policies prompted … [...]
Meta has quietly introduced a way for Australians to stop their user data from training its AI model. But the company never announced the change, leaving the choice effectively hidden [...]
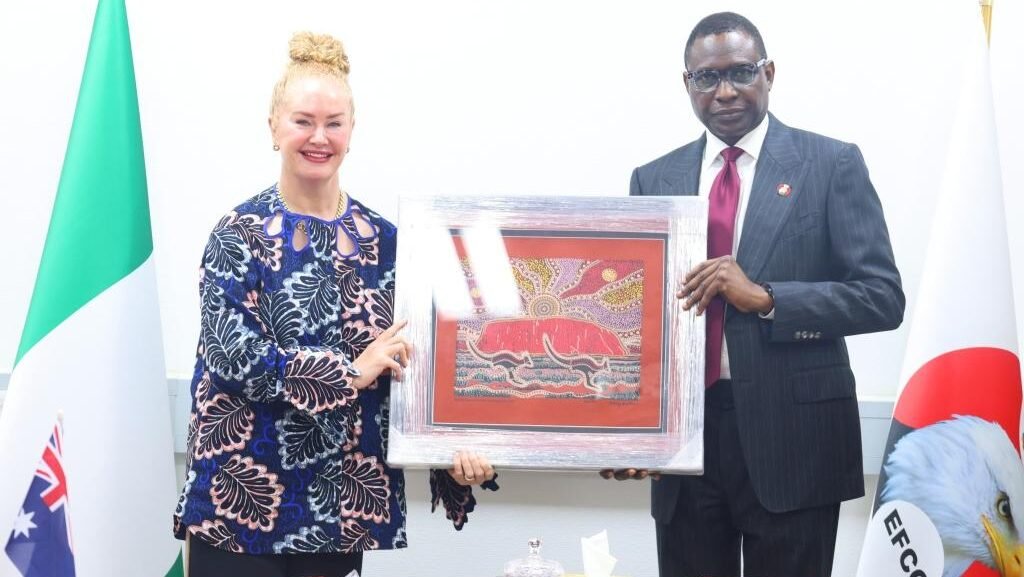
The Economic and Financial Crimes Commission (EFCC) and the Australian Federal Police (AFP) have signed a memorandum of understanding (MoU) to … [...]
Australia’s privacy watchdog has found employees of an India-based subcontractor accessed a limited number of recordings and transcripts, but will … [...]
Key points The OAIC will not investigate VIQ Solutions despite finding a reasonable basis for concern over a possible APP 11 breach, citing VIQ's … [...]
Key points NSW Police's Cybercrime Squad is investigating an alleged data breach at NSW Health, alerted at about 1pm on Friday October 30. • Cyber … [...]
Potentially sensitive documents have been stolen from NSW Health in a major cybersecurity breach. The NSW Health website impacted by the breach is the Oral Health Fee For Service Scheme. [...]
NSW Health has been hit by a cyber breach, with the department declaring it a major incident. Officials confirm no patient data has been impacted and only a limited amount [...]
Senator Penny Wong has announced a new role for the senior Australian Signals Directorate officer. • Tue, 03 Nov 2026 • Government *]:clear-none … [...]
The luxury auctioneer has been in touch with impacted clients; “no evidence” that credit card details or passwords were impacted. • Tue, 03 Nov 2026 • … [...]
Bendigo and Adelaide Bank is in a legal tangle after a scammer stole more than $6 million from a 97-year-old widow. • Mon, 02 Nov 2026 • … [...]
More than 120 people were arrested during a five-month police trial using live facial recognition technology. Police scanned 1.3 million faces during … [...]
 Confirmed 08-Nov-26 AU VIC
Who Gives A Crap confirms customer data exposed in software breach
Customers of Australian toilet paper company Who Gives A Crap (WGAC) have been told their personal information may have been accessed in a third-party cyber security incident. The data included customers' first and last names, email addresses, phone numbers, mailing addresses and the total amount spent with the company.
 Claim 05-Nov-26 AU QLD
[Unconfirmed] Ransomware group Qilin, has claimed to have breached Queensland school, Calvary Christian College
Calvary Christian College was listed on the qilin ransomware leak site in November 2026. The organisation operates in the Education sector in Australia. The listing contained no supporting evidence of the breach.
 04-Nov-26 AU
ACMA, Telcommunications, Spam Act 2003
SpinTel pays $653K penalty for spamming former customers
Australian telco SpinTel Pty Ltd (SpinTel) has paid a $653,400 penalty after sending more than 32,000 commercial emails without consent. An Australian Communications and Media Authority (ACMA) investigation found that between July and September 2025, SpinTel sent marketing emails to former customers encouraging them to return to the telco and promoted its products, including its NBN and mobile service plans.
 Claim 04-Nov-26 AU VIC
[Unconfirmed] Prospect Hill Camberwell , a retirement village based in Australia has been listed by SafePay ransomware group
Threat actor SafePay has listed Victorian based retirement village operator, Prospect Hill Camberwell, as being breached by their teams. No corroborating information has been provided.
 Claim 04-Nov-26 AU Qld
[Unconfirmed] The Southern Cross Digital an Australian ad management company, has been listed by Soul ransomware group
Southern Cross Digital a Google and Facebook ad management for Queensland businesses, has a data breach listed by threat actor group Soul. The breach has not been independently verified.
 Confirmed 04-Nov-26 AU NSW
Police investigate cybersecurity breach of NSW Health's Oral Health Fee For Service Scheme website
The NSW Health website impacted by the breach is the Oral Health Fee For Service Scheme. Police are investigating the incident, with Cyber Security NSW saying no patient data has been compromised.
 Confirmed 03-Nov-26 AU NSW
Exclusive: Sydney-based First State Auctions customer data impacted by cyber incident
A Sydney-based luxury auction house, First State Auctions, has confirmed it recently responded to a cyber security incident after it was mentioned in connection with a data breach on a popular underground hacking forum.
A hacker posting under the name sexyskin claimed to be in possession of more than 1 million lines of customer data comprising names, emails, phone numbers, and address details in October.
 Published 03-Nov-26 AU NSW
Qantas customer data possibly exposed in Amadeus hack
Qantas says it has been potentially impacted by a data breach affecting global travel technology provider Amadeus. Amadeus, which services around 141 global airlines, has reportedly advised its clients that no payment or financial data was accessed, though other personal details may have been exposed.
 Confirmed 02-Nov-26 AU VIC
HealthShare’s $50M Tender Dies After Pricing Leak
The HealthShare Victoria tender breach involved a data leak that exposed confidential pricing spreadsheets of competing bidders. This breach, which occurred over a multi-month period, was caused by a human error by one medical device company that accessed the pricing information multiple times. The breach was discovered in August 2026, after a supplier raised the alarm in February. The company, referred to as the "disclosee" in government correspondence, was allowed to continue competing for the contract despite the breach. HealthShare Victoria terminated the tender process to ensure competitive fairness, but bidders were not compensated for their preparation costs.
If you believe any information in this post is inaccurate or incomplete, please contact us so we can review the matter. Parties with additional relevant information relating to the incident are also invited to get in touch.

Australian Insurer Ransomware Attack, 07 January 2026 Queensland-based rental car insurer Prosura...

Australian Medical Ransomware Attack, 06 Jun 2025: Victorian based Ascot Vale Health Group targeted by Global ransomware group. Global ransomware group has so far not listed how much data it has allegedly stolen or what kind of data may have been compromised.

Australian Racing Industry Ransomware Attack, 05 Jun 2025: Victorian based RISE Racing confirms Sarcoma ransomware attack. Reports indicate that 1.6GB of sensitive data was stolen, including: Banking details, financial records, participant personal information and operational data related to the racing industry.

Australian Accounting Firm Ransomware Attack, 16 May 2025: Victorian MKA Accountants confirms Qilin ransomware attack. Qilin published 12 documents as part of its leak post, including internal correspondence, financial statements, and insurance information

Australian Cyber Incident – Court Data Breach, 26 March 2025: NSW court website involved in major data breach, 9,000 documents downloaded. Man charged in connection with court document data breach.

Incident – Law Firm Ransomware Attack, 13 March 2025: Prominent Sydney law firm Brydens Lawyers reveals a serious cyber incident in the wake of a February intrusion into its network. More than 600 gigabytes of data – including case, client, and staff data – was stolen in the incident.

NZ Incident – Ransomware Attack, 28 February 2025: DragonForce Ransomware Targets Kiwi Car Dealership Tristram European. The attackers claim to have stolen over 30 gigabytes of sensitive data, including customer information and financial records.

Updated Incident – Medical Data Breach, 19 February 2025: Australian IVF provider Genea in cyber incident. Genea patients frustrated by lack of communication amid data breach.

Incident – University Ransomware Attack, 16 February 2025: Australian National University investigating alleged cyber attack by FSociety ransomware group. No ransom amount was given; however, society is threatening to publish the data within seven days.

NZ Incident – Medical Ransomware Attack, 13 February 2025: KillSec claims ransomware attack on New Zealand based Obex Medical. While the exact details of the breach remain unclear, this latest incident highlights the persistent threat of ransomware groups, particularly those focused on industries like healthcare.


“You cannot escape the responsibility of tomorrow by evading it today.” –...


